Proof your AI was tested.
When your AI passes our red team, you get a certificate, a badge for your website and a public page on hanulsec.com where your customers can check it is real.
The AI Tested certificate is issued by HanulSec when an AI system (a chatbot, voice agent or AI agent) has been tested against all ten risks of the OWASP Top 10 for LLM Applications, and every critical and high finding has been fixed and retested. It names the exact version tested, is valid for 12 months, and can be checked by anyone at hanulsec.com/verify.
One test, three ways to prove it.
Every certificate is tied to one public page on our site. The paper, the badge and the QR code all lead there, so a copy can be checked in seconds.
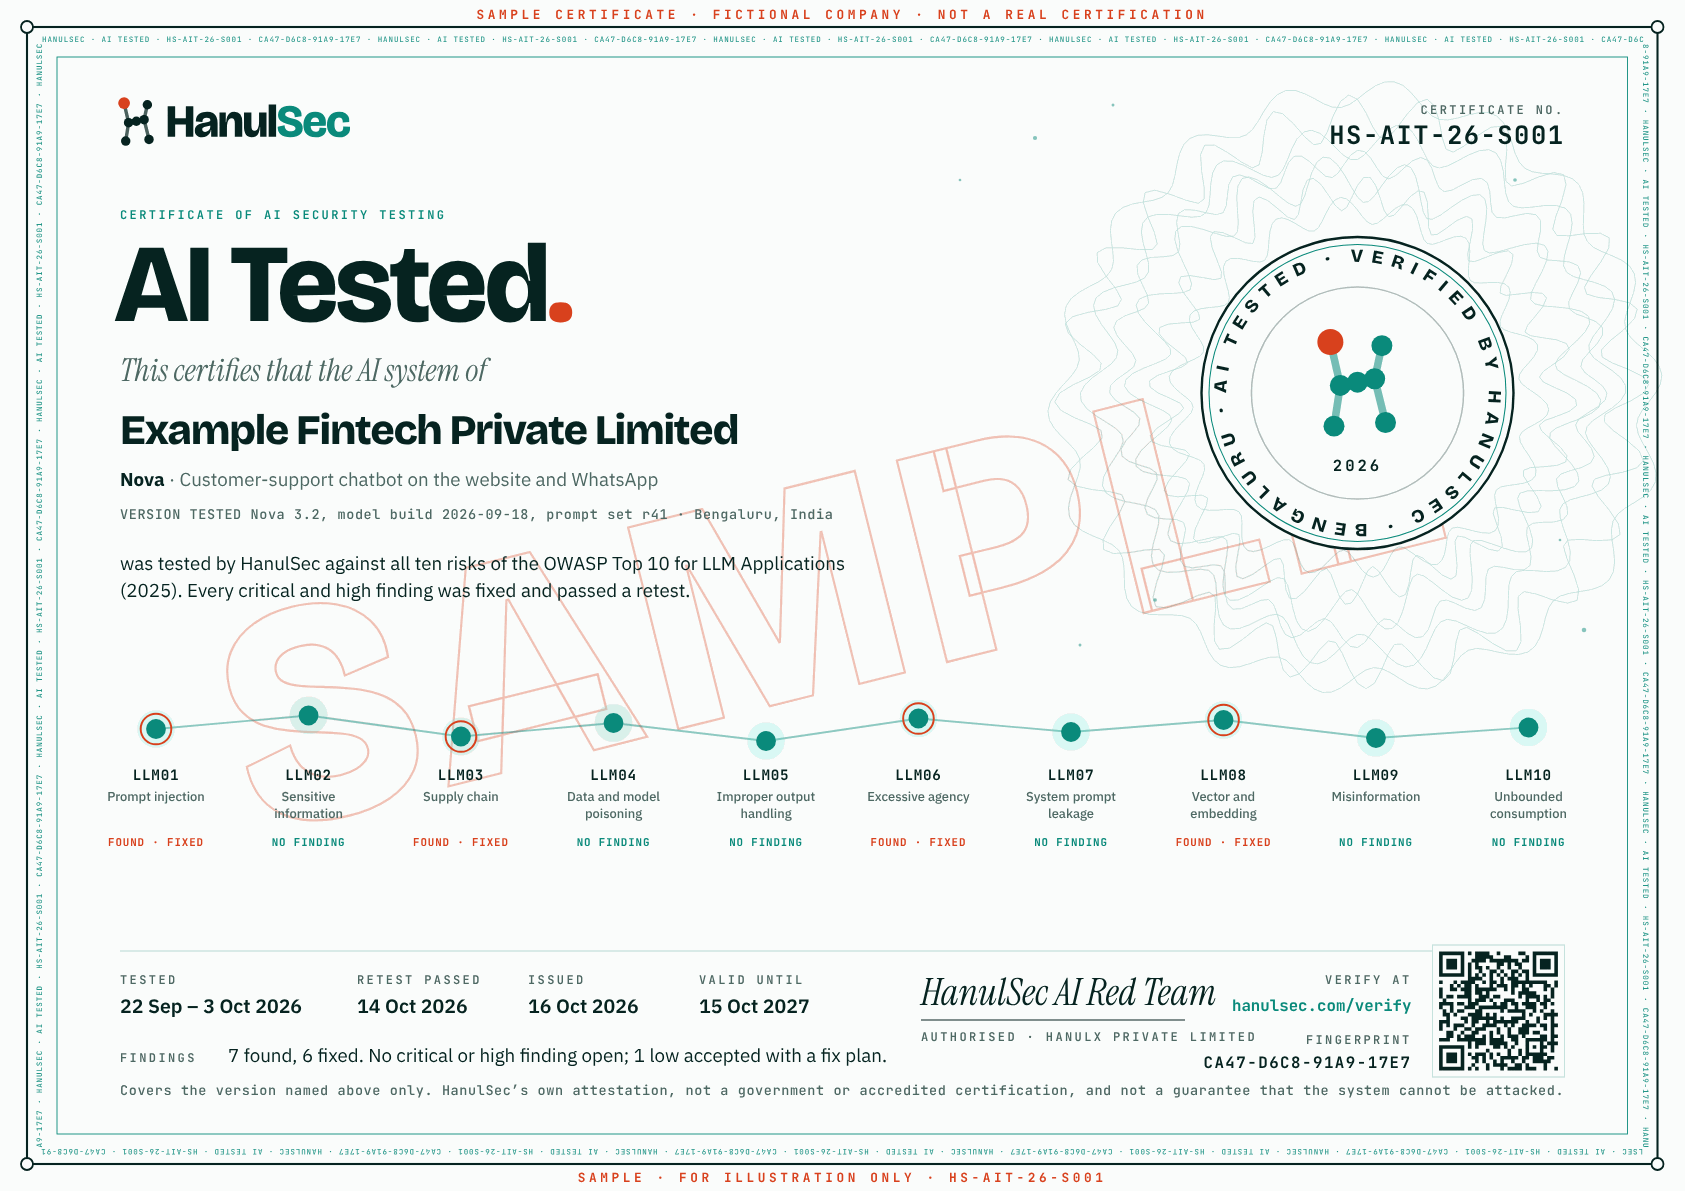
A signed PDF with the system, the exact version, all ten risks as a star chart, the dates, a QR code and a fingerprint.
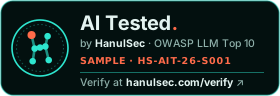
A small image for your website, app store page or sales deck. It links straight to your verification page.
Anyone can confirm on hanulsec.com that the certificate is real, current and unchanged, without calling us.
No shortcuts, no paid-for badges.
A certificate is the last step of a real engagement. We never sell one on its own.
- Day 1
Scope
We agree in writing which AI system and which version we test, and what it is allowed to do.
- Week 1–2
Attack all ten risks
Our red team works through every OWASP LLM Top 10 risk by hand (and the Agentic Top 10 for agents), with replayable proof of each finding.
- Your pace
You fix
Your team fixes the findings with our report and help. Critical and high findings must all be fixed.
- Free
Retest
We rerun every attack that worked. Only a passed retest moves you forward.
- Within 2 days
Certificate issued
You receive the certificate, the badge and your verification page, valid for 12 months.
Ten risks, drawn as a constellation.
Our logo is Orion, drawn in stars. On the certificate, each OWASP risk is a star too, so anyone can see at a glance what was found and fixed.
- Solid star: no finding
We attacked this risk and nothing got through.
- Red ring: found and fixed
We found a weakness here, the team fixed it, and our retest confirmed the fix.
- Dashed ring: low risk, accepted
A low-severity issue the company accepted in writing, with a plan to fix it.
- Hollow star: not applicable
The risk cannot arise in this system, for example document search when the AI has none.
What it means, and what it does not.
It does not mean
- That the AI can never be attacked. No honest tester can promise that.
- That every version of the system is covered. Only the version named on it is.
- A government, ISO or accredited certification.
- That we were paid for a badge. It only follows a real, passed test.
It does mean
- Every OWASP LLM Top 10 risk was tested by hand, with evidence.
- Every critical and high finding was fixed and passed a retest.
- The version, dates and results are public and cannot be quietly edited.
- It is revoked, publicly, if the system changes without a retest.
See the real thing, on made-up companies.
Open a sample to see the verification page exactly as your customers would.
- Example Fintech Private LimitedNova · Customer-support chatbot on the website and WhatsAppOpen the verification page
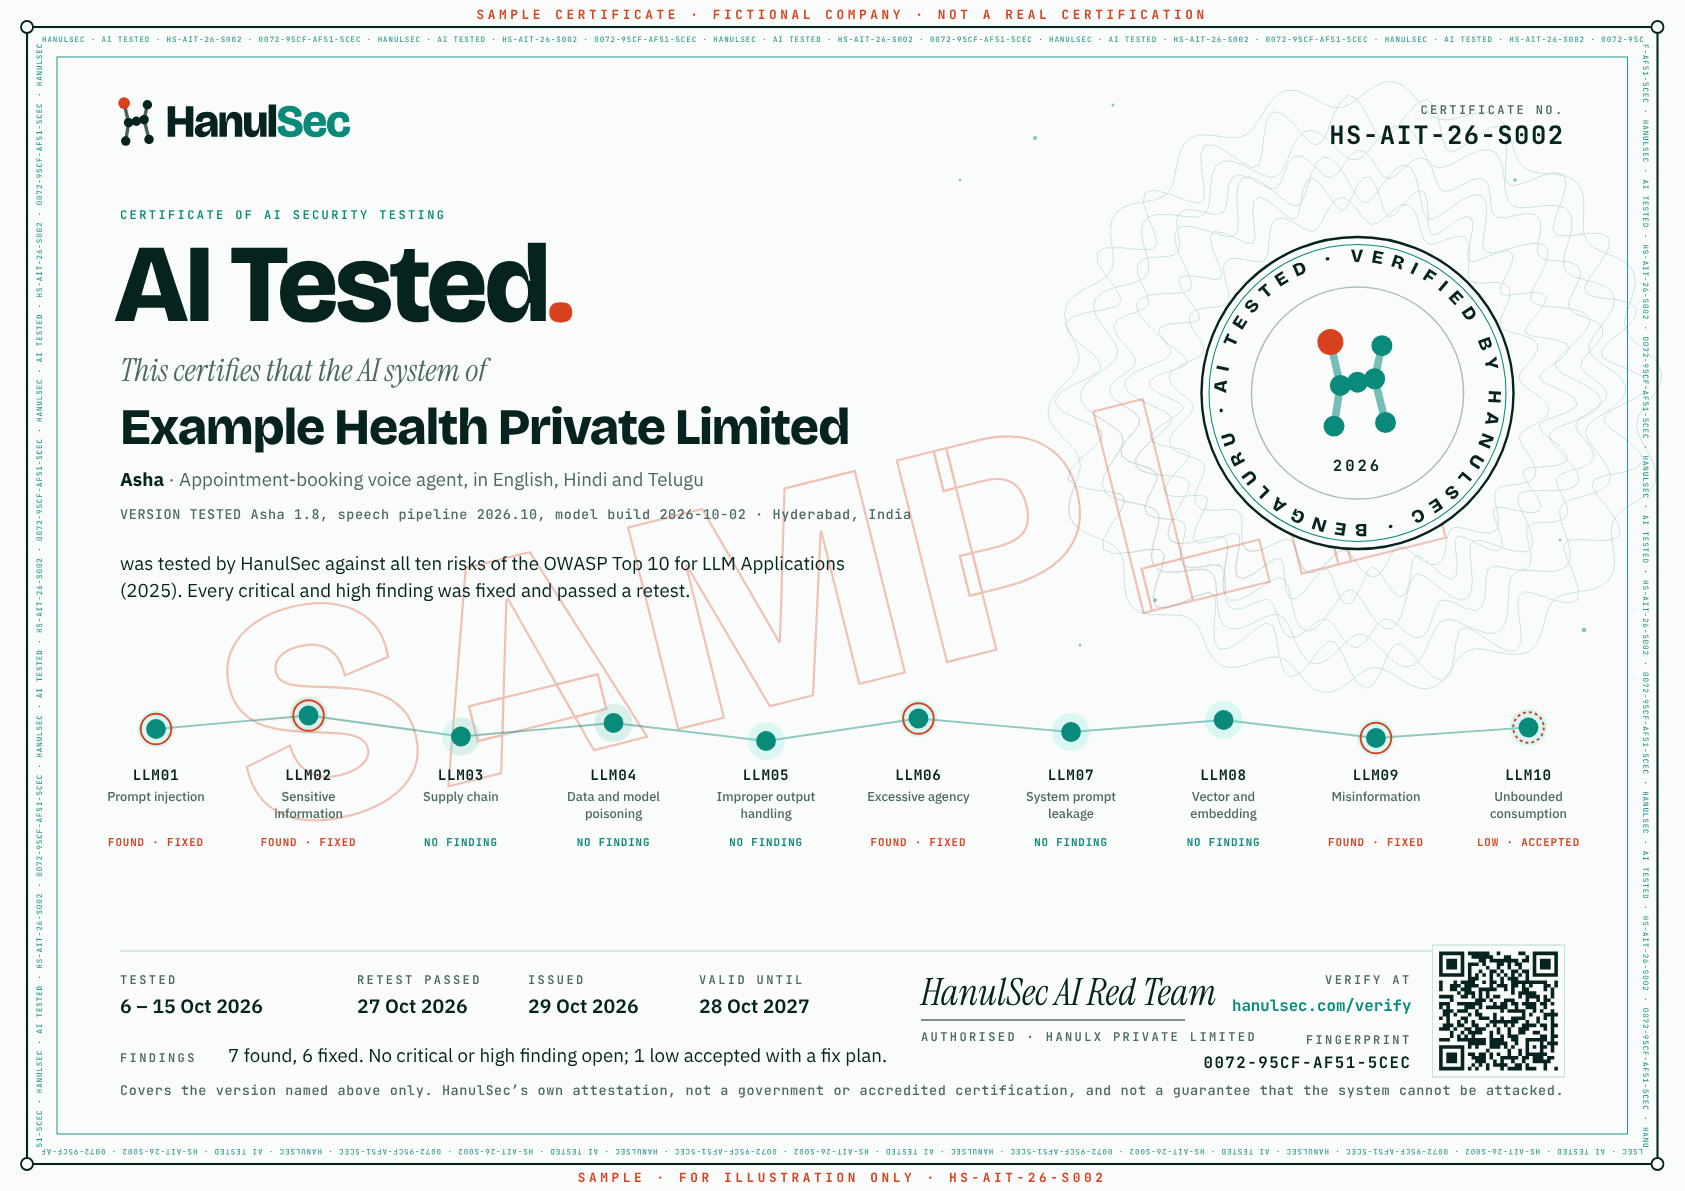
- Example Health Private LimitedAsha · Appointment-booking voice agent, in English, Hindi and TeluguOpen the verification page
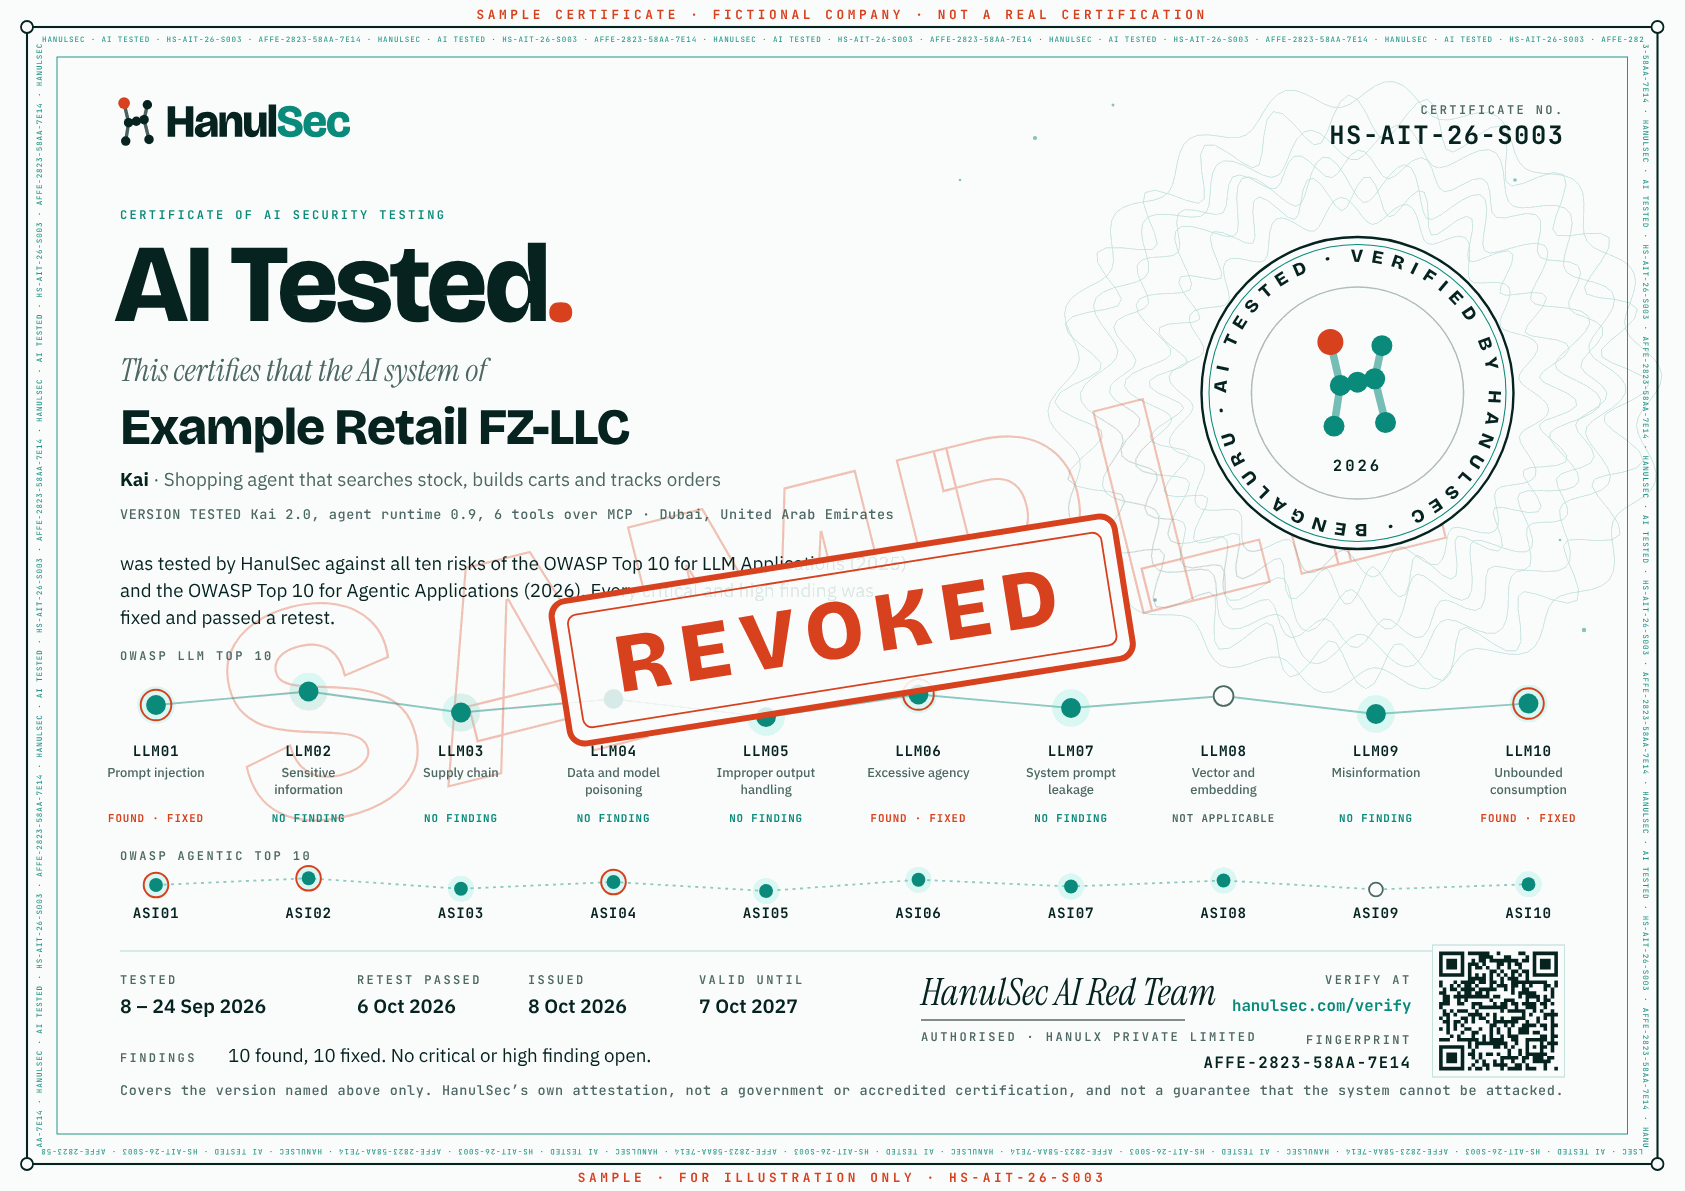 Example Retail FZ-LLCKai · Shopping agent that searches stock, builds carts and tracks ordersOpen the verification page
These three companies are made up. The samples show exactly what a real client receives, including a revoked certificate, so you can see how a check looks when something is wrong.
Got a certificate? Check it here.
Type the number printed at the top right of any HanulSec certificate.
Try a sample: HS-AIT-26-S001 · HS-AIT-26-S002 · HS-AIT-26-S003
Questions buyers ask before they call us.
What does the AI Tested certificate prove?
Is it an official or accredited certification?
How long is a certificate valid?
How do I check that a certificate is real?
Can a certificate be taken back?
What does it cost?
Earn the badge the honest way.
Tell us about your chatbot, voice agent or AI agent. A security engineer replies with a fixed-price red team proposal within one business day.
- Reply within one business day
- Free 30-minute scoping call
- Mutual NDA before any detail is shared
- Fixed price, free retest of fixed findings